

Top 7 Cloud DDoS Protection Providers for 2026
Why DDoS Protection Is Critical in 2026 As businesses migrate more critical operations to the cloud, DDoS attacks have become
Why DDoS Protection Is Critical in 2026 As businesses migrate more critical operations to the cloud, DDoS attacks have become
As businesses rapidly adopt cloud-native architectures—powered by Kubernetes, containers, and microservices—securing these highly dynamic environments has become more complex than

In the current digital environment, safeguarding your web applications and APIs is imperative, not optional. As cyber threats become increasingly
Cloudflare WAF is a popular choice in the cybersecurity landscape, but it isn’t a one-size-fits-all solution. In 2026, organizations are
As the cybersecurity landscape evolves rapidly in 2025, safeguarding web applications grows increasingly complex and vital. The rise in zero-day
Key Takeaways API gateway security is the set of controls, mainly authentication, authorization, and rate limiting, that a gateway applies
Reporting Convention New this week refers to vulnerabilities, exploits, or incidents disclosed between September 9–16. Active-exploitation update signifies an older
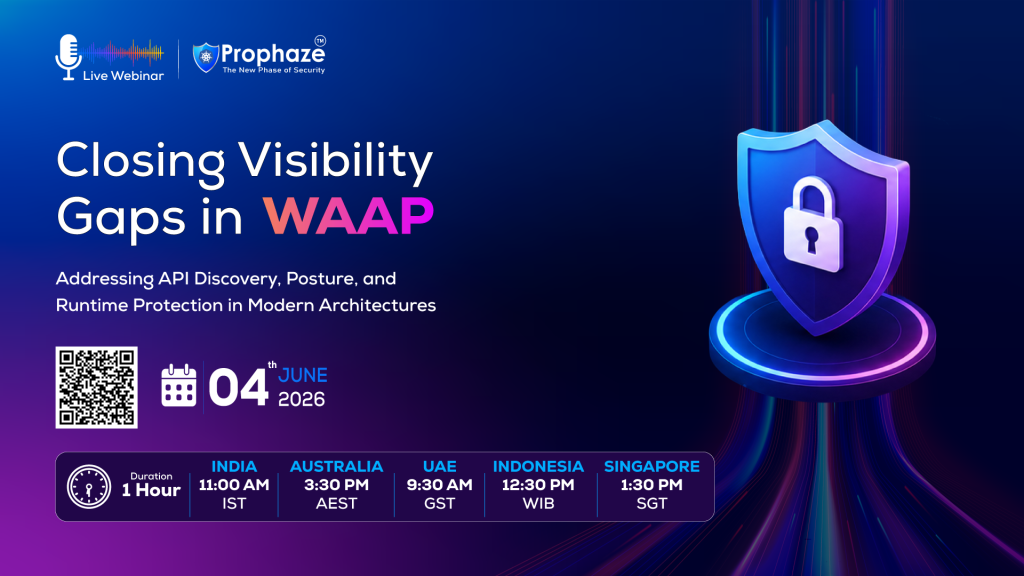
Closing Visibility Gaps in WAAP Addressing API Discovery, Posture, and Runtime Protection in Modern Architectures Thursday, 4th June 2026 12:00
Two decades ago, security meant building a wall. Today, the wall is gone. Every AI feature ships as an API.

The Week in One Line An actively exploited, unauthenticated CVSS 10.0 Magento/Adobe Commerce RCE forced Adobe to issue an emergency